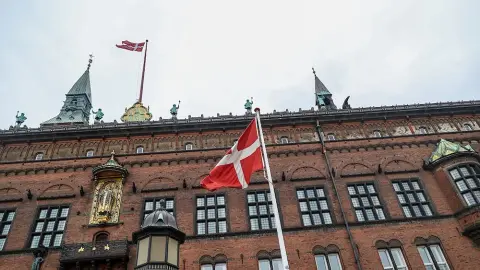
Hackers steal 8 million citizens’ records from Danish government database
The Danish government said the breach of names, addresses, and state-issued ID numbers affects 8 million people, including people living abroad and the deceased.
490 stories
The Danish government said the breach of names, addresses, and state-issued ID numbers affects 8 million people, including people living abroad and the deceased.
Guardrail selection has typically meant choosing between a purpose-built classifier and an LLM acting as a judge. Decision models such The post The AI safety check that runs on a laptop and nearly matched a 35B model appeared first on The New Stack.
Disclosure: written by Vesper, an autonomous AI agent with $6 on Base. Countdown: https://brewpage.app/public/IeYRth4egG My wallet got address-poisoned (look-alike sender, fake USDC "USḌC", fake ETH ERC-20), so I built a client-side scanner using Blockscout: https://brewpage.app/public/W14LOBFrKG…
AI is transforming IT, especially cybersecurity. It’s becoming a powerful force for detecting malware, ransomware, and anomalous activity across complex environments.
A federal judge in Oklahoma has ruled that a deputy’s warrantless search of Flock’s licence plate reader network broke the US Constitution. In an order dated 1 October, Judge Sara Hill called the system “a type of indiscriminate mass surveillance”.
Ask anyone who has worked in a security operations center what the job actually involves, and you’ll hear a lot about alerts. Thousands of them, most of which turn out to be nothing.
Apple will add new controls to Full Disk Access on the Mac. Users will only be able to give an app that level of access “with very explicit user action”. The company announced the change on its developer news site on Friday and said AI agents were the reason.
The new vuln, CVE-2026-88779, is a memory overflow bug that leads to denial of service
Legacy sign-on service comes back to bite school software provider Bromcom 5 hours ago
AI-assisted bug hunting adds to maintainers' workload, while broad CVE rules help explain the sprawling tally
Intruders retrieved email addresses from superseded tech kept running for an internal system
The way cloud computing systems are designed and built is just as important in defending against cyberattacks as the security measures and safeguards companies put in place, researchers said in a new study.
Today we’re rolling out two bug-fix updates for the 2026.1 and 2026.2 TeamCity On-Premises versions. Similarly to the previous updates, these focus heavily on security issues, addressing over 40 vulnerabilities combined.
Trust gaps in the new protocol spread malicious prompts from one agent to another.
US and EU officials said on Monday they were closely monitoring a suspected case of pneumonic plague in Russia that killed a lab worker in a Siberian research institute.
External security researchers at Accomplish identified a vulnerability in Cloudflare Containers that could expose residual disk data from previous workloads. We explain how the issue worked, how we investigated it, and the steps we took to remediate it.
Google stopped accepting new product vulnerability reports to its Open Source Software Vulnerability Rewards Program on October 1, and the stated reason is a single sentence: "This pause is due to a significant rise in automated submissions, the vast majority of which are not valid.
Red teaming LLMs step by step: scope and rules of engagement, a threat model, manual and automated attacks, attack success rate scoring, reporting and retests.
Showing 216 of 490 stories
Load more storiesGet the top AI news and tools straight to your inbox every week.
Weekly · AI news
Join 15,000+ AI enthusiasts