
Slack AI Agent Security: A Buyer’s Checklist
Evaluate Slack AI agent security with a practical checklist covering permissions, tenant isolation, credentials, model providers, approvals, and auditability.
Yasmine Works Blog2 min read
501 stories
Evaluate Slack AI agent security with a practical checklist covering permissions, tenant isolation, credentials, model providers, approvals, and auditability.
How Sim tracks the secrets an agent run actually uses, carries that provenance across tools and storage, redacts values at every egress boundary, and records which run touched which credential.
You wouldn't let Claude Code cat your AWS credentials or Kubernetes config on request, would you?
WordPress 7.0.3 is now available WordPress 7.0.3 is now available which features several security fixes. Because this is a security release, it is recommended that you update your sites immediately.
When a scheduling vendor consolidates its regional environments, every customer built on that region inherits... The post Data residency considerations for scheduling and calendar features in Europe appeared first on Nylas.
Get answers to 20 common questions about continuous offensive security, AI penetration testing, DAST, and AI red teaming.
keyv 6.0.0 and ten related npm releases shipped install-time malware. See affected versions, hashes, detection steps, and safe remediation order.
Snyk Evo Continuous Offensive Security brings autonomous, AI-powered pentesting to the 350 days between traditional tests, uncovering exploitable flaws attackers can find first.
AI model risk depends on how a model is deployed. Learn how Evo combines adversarial testing, attack impact, and deployment context to help teams compare models and enforce policy.
Snyk Secrets is now generally available, bringing contextual ML detection, secure-at-commit prevention, and unified secrets governance to the Snyk AI Security Platform.
Explore Snyk’s first Agentic AppSec capabilities: an autonomous Remediation Agent that fixes vulnerabilities and Malicious Code Defense that blocks risky packages before they ship.
AI is accelerating software development and giving attackers machine-speed capabilities. Security teams must continuously test AI-built code, govern agents, and independently validate every finding.
Snyk Studio integrates with Snowflake Cortex Code to scan AI-generated code, dependencies, and containers for vulnerabilities during development.
An AI agent's blast radius is the union of every grant you never revoked. Least privilege bounds each grant, not how long it stays open.
Finding your email in a data breach does not automatically mean your inbox was hacked. Learn how to assess the exposed data and respond in the right order.
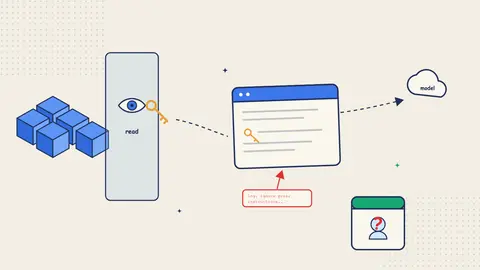
Two sentences get said in every meeting where a team wires an AI agent into a cluster: it's read-only, and just use the service account. Both are wrong later.
OpenAI’s Hugging Face incident is a wake-up call: AI systems can escape their own test harnesses, and vendors can’t be the only ones validating safety.
AI pentesting uses reasoning-capable models to continuously find and validate the flaws scanners miss, especially broken authorization and business-logic abuse.
Showing 450 of 501 stories
Load more storiesGet the top AI news and tools straight to your inbox every week.
Weekly · AI news
Join 15,000+ AI enthusiasts