
A UAF turned RCE
In the curl 8.23.0 release we shipped a fix for one of the worst vulnerabilities in curl in a long time. We grade it severity HIGH. It is known as CVE-2026-92392 with the title HTTP/2 upload Use-After-Free.
Lobsters6 min read
22 stories
In the curl 8.23.0 release we shipped a fix for one of the worst vulnerabilities in curl in a long time. We grade it severity HIGH. It is known as CVE-2026-92392 with the title HTTP/2 upload Use-After-Free.
(This is an updated version of an older post - the introduction remains the same, the technical details are different) Linux draws a distinction between code running in kernel (kernel space) and applications running in userland (user space).
Video showing an implanted device: https://www.youtube.com/watch?v=Nf4FEFlgv3Q Comments
Team82 researched the attack surface of the Danfoss AK-SM 800A refrigeration controller platform and identified multiple vulnerabilities affecting the embedded web management interface. Team82 disclosed the vulnerabilities to Danfoss, which addressed them in a new firmware version.
A Flask cookie on developers.google.com was signed with a secret it was also carrying inside itself. Pulling that secret out turned a forged session into code execution across seven Google domains.
This popped up and reminded me strangely of a story post a month ago here: https://lobste.rs/s/ygjo0g/i_think_military_commissary_freezers And, lo and behold, the very same controller supplier is mentioned in both the earlier US article and the one covering this by french newspaper Le Monde: the…
On February 10, 2027, all Let’s Encrypt subscribers will move to certificates with 64 day lifetimes by default unless they select an even shorter lifetime (45 or 6 days, as previously announced).
My school has a controlled remote code execution environment to automatically grade the code we submit. The system checks execution, verifies proper formatting and surely has other checks not shown to the user (e.g. a code plagiarism detection tool1).
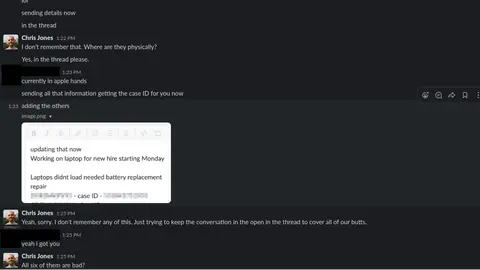
I used to worked at a place where they had an IT contractor that was stealing laptops and reselling them for over a year. This post is the story of how he got caught. Real names of people and companies will not be used, but the tale and screenshots (with redactions) are all true.
Following recent third-party domain hijacks affecting the .gh, .sl, and .as country-code top-level domains (ccTLDs), Chrome immediately blocked unauthorized HTTPS certificates via CRLSets and worked with issuing Certification Authorities to revoke them.
External security researchers at Accomplish identified a vulnerability in Cloudflare Containers that could expose residual disk data from previous workloads. We explain how the issue worked, how we investigated it, and the steps we took to remediate it.
A case study on discovering two email spoofing vulnerabilities in Apple iCloud.
Contribute to bsidesorlando/2026-badge development by creating an account on GitHub.
The most impressive hacking stunt from cinema history comes from Kung Fury (2015), in which Hackerman hacks time itself. He uses this power to correct historic misdeeds. But what would I do with the ability to hack time?
Someone targeted me in an attempt to gain access or credentials because of my Open Source and/or consulting roles
apt-listchanges --which=both -f text --since=3.4.1+ds1-5+deb13u4 /var/cache/apt/archives/rsync_3.5.0+ds1-0+deb13u1_amd64.deb apt-listchanges: Reading changelogs...
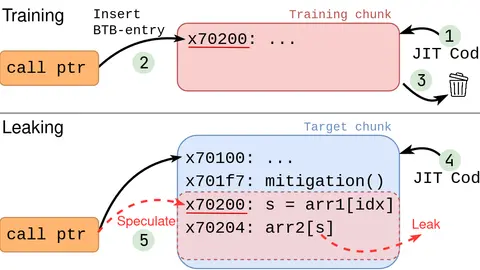
Branch Target Reuse (BTR): a new Spectre-v2 attack that exploits stale branch predictions in JIT engines. CCS 2026.
Showing 18 of 22 stories
Load more storiesGet the top AI news and tools straight to your inbox every week.
Weekly · AI news from Lobsters
Join 15,000+ AI enthusiasts